Global Knowledge
Security knowledge from SIRP curated doctrine and recognized security references.
Ask: What does APT38 typically target?
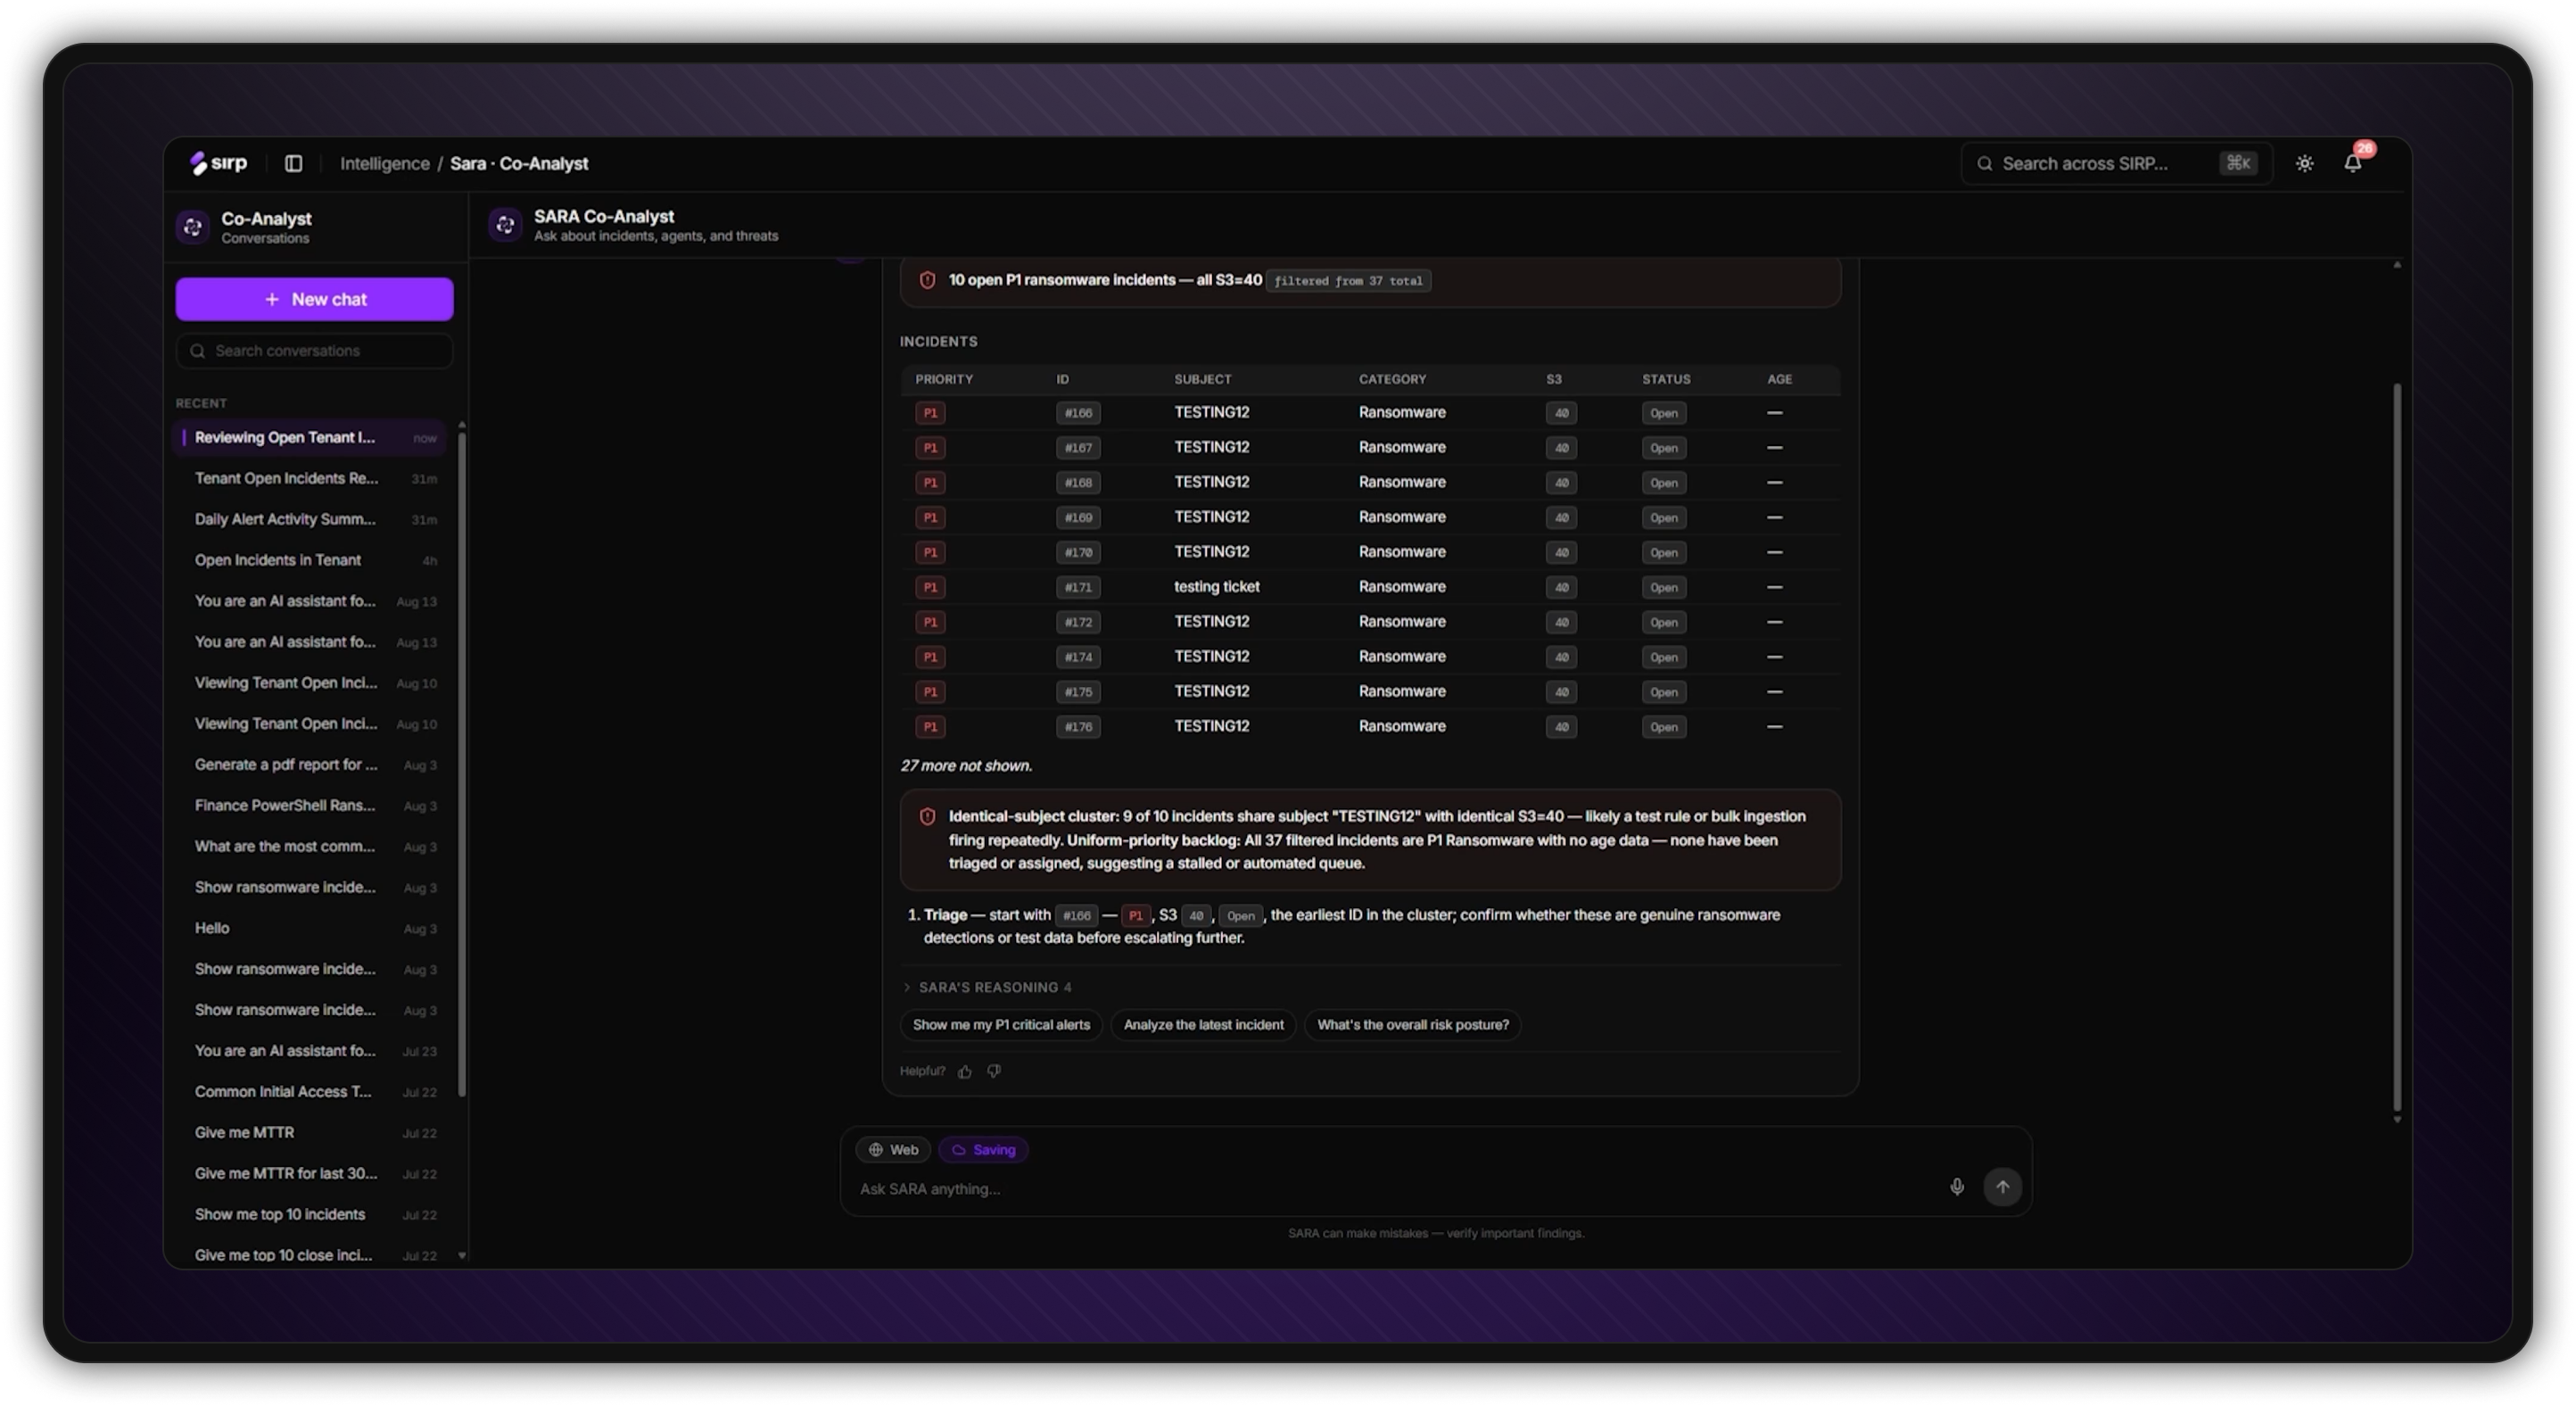
Sara is the Co-Analyst inside OmniSense. When a case needs a human call, Sara explains what OmniSense found, why it recommends the next step, and where every piece of evidence came from.
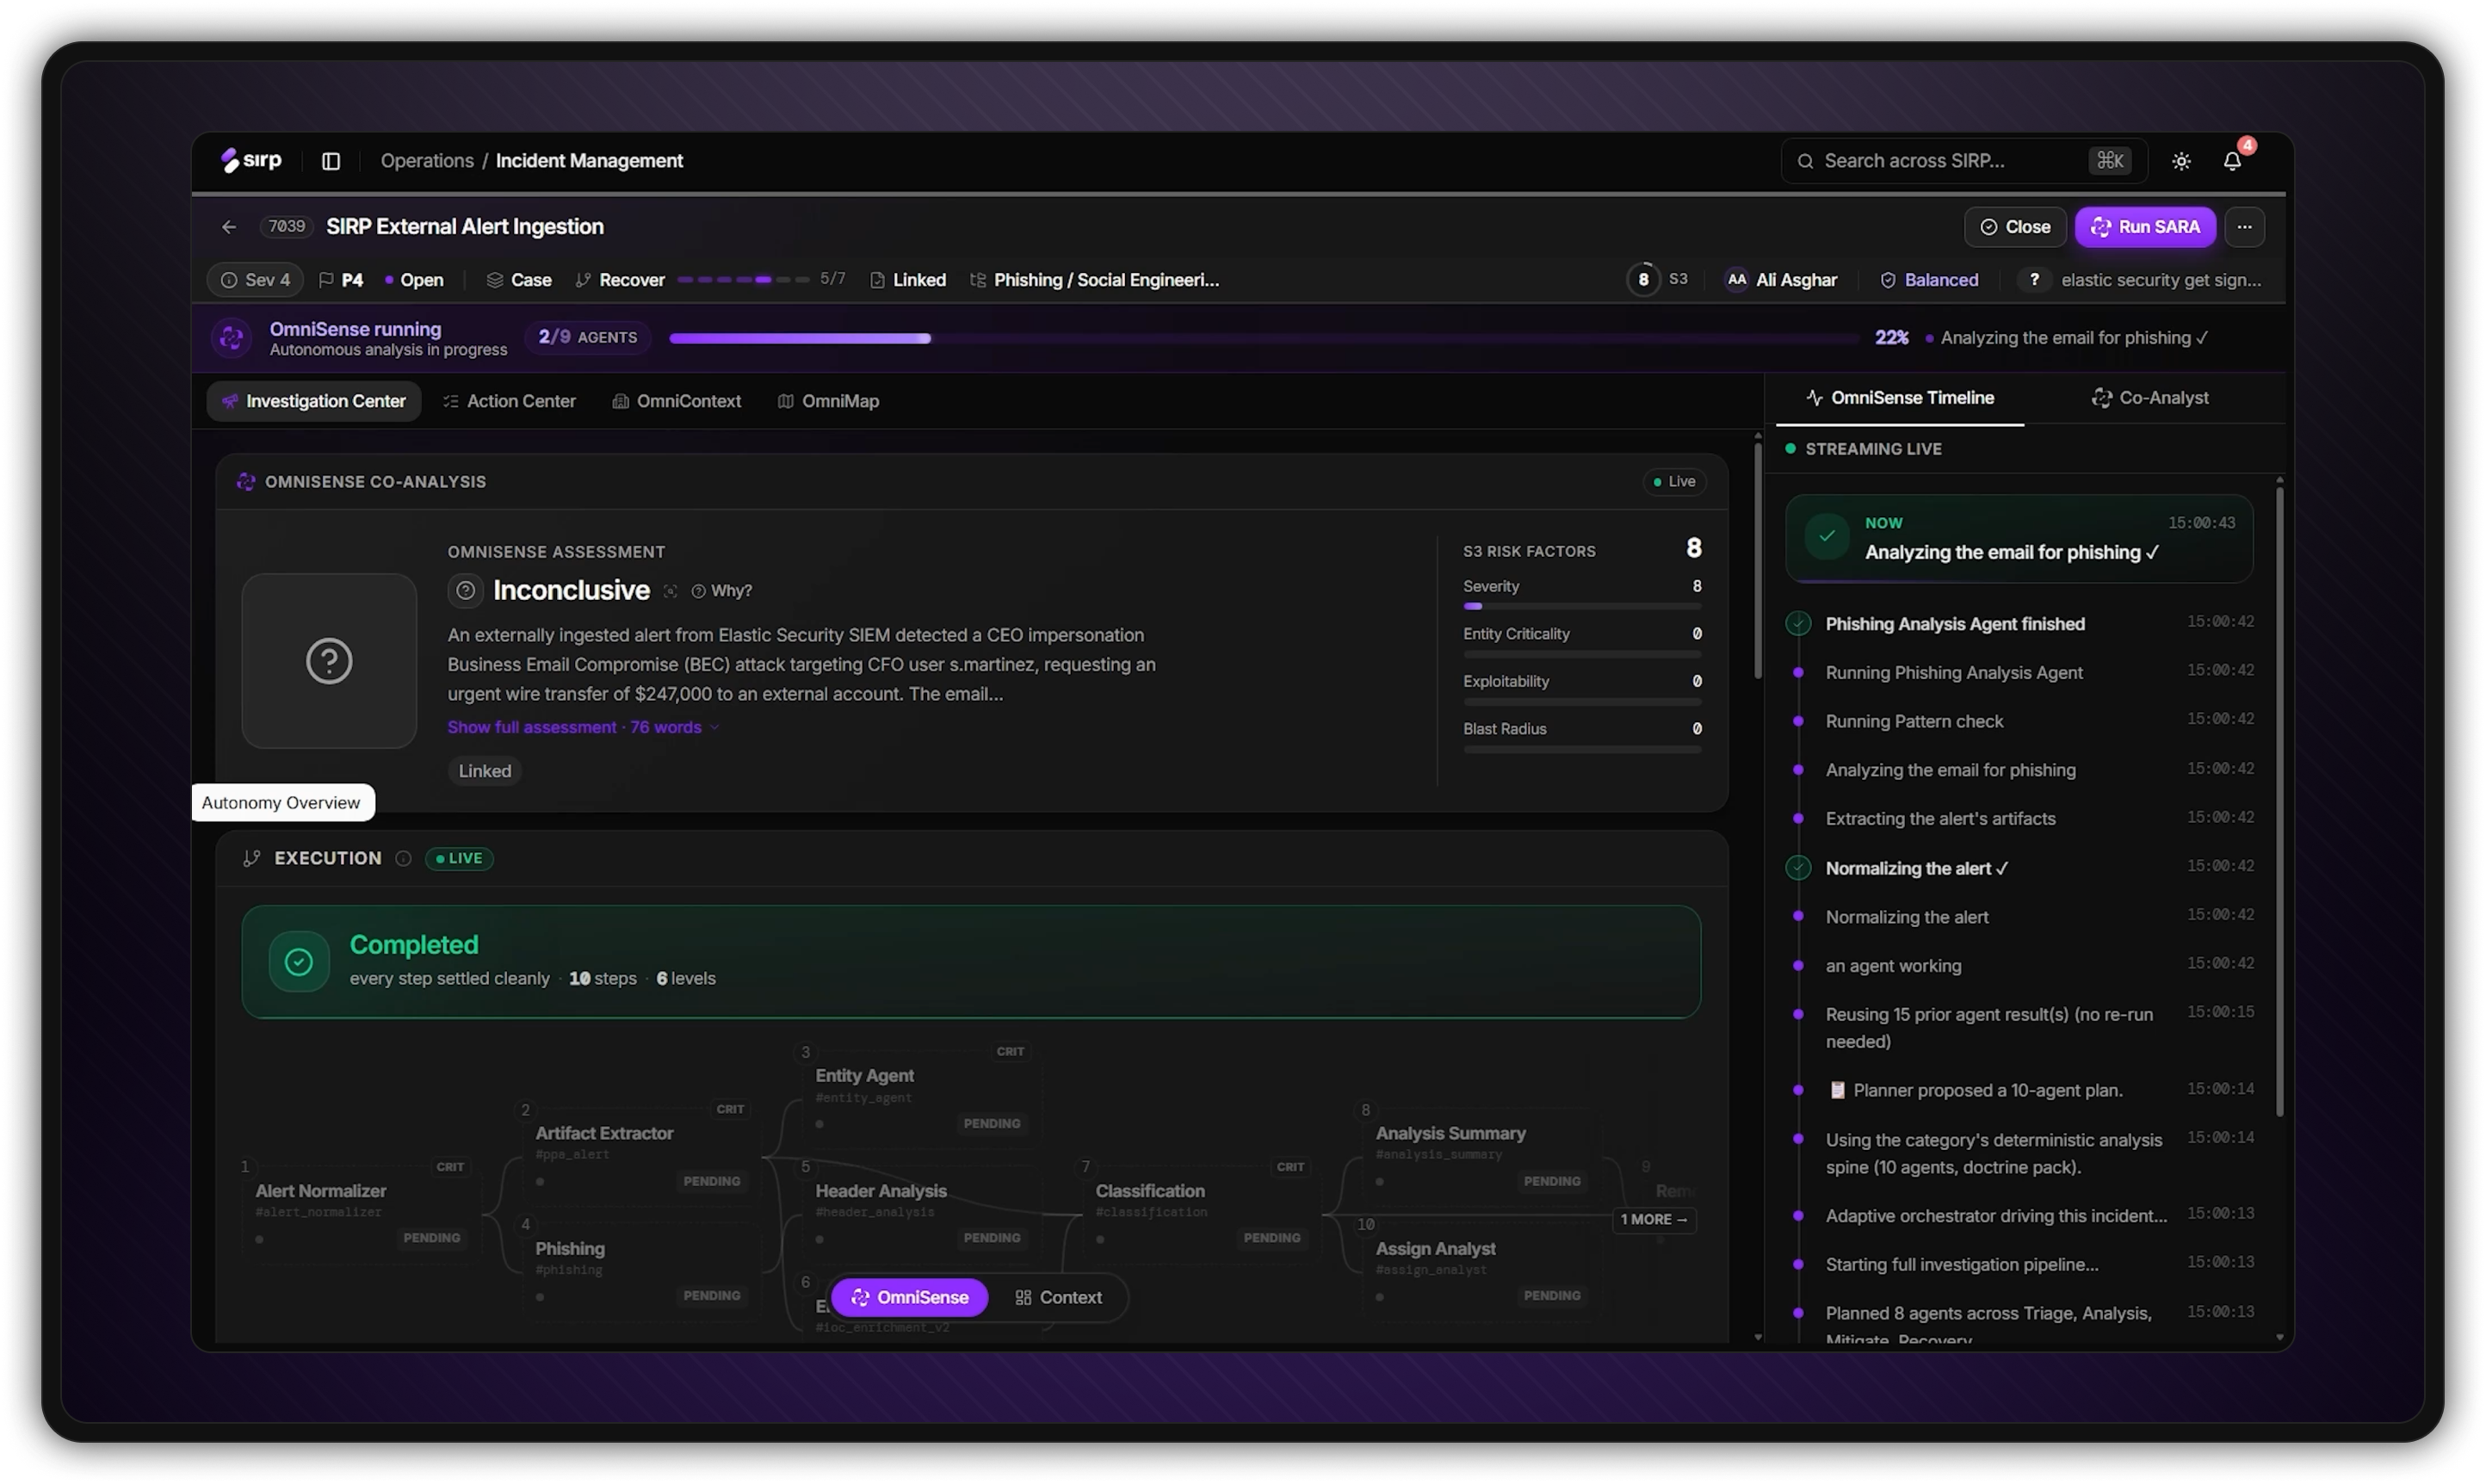
An analyst opens a case. The verdict, confidence, evidence, and recommended
response are already in the OmniSense workbench. They ask Sara why, check the
sources, and approve or decline the gated action without leaving the conversation.
The decision happens in the conversation, and goes on the record with it.
Sara starts with the context closest to your security operation
and reaches outward only when it needs to.
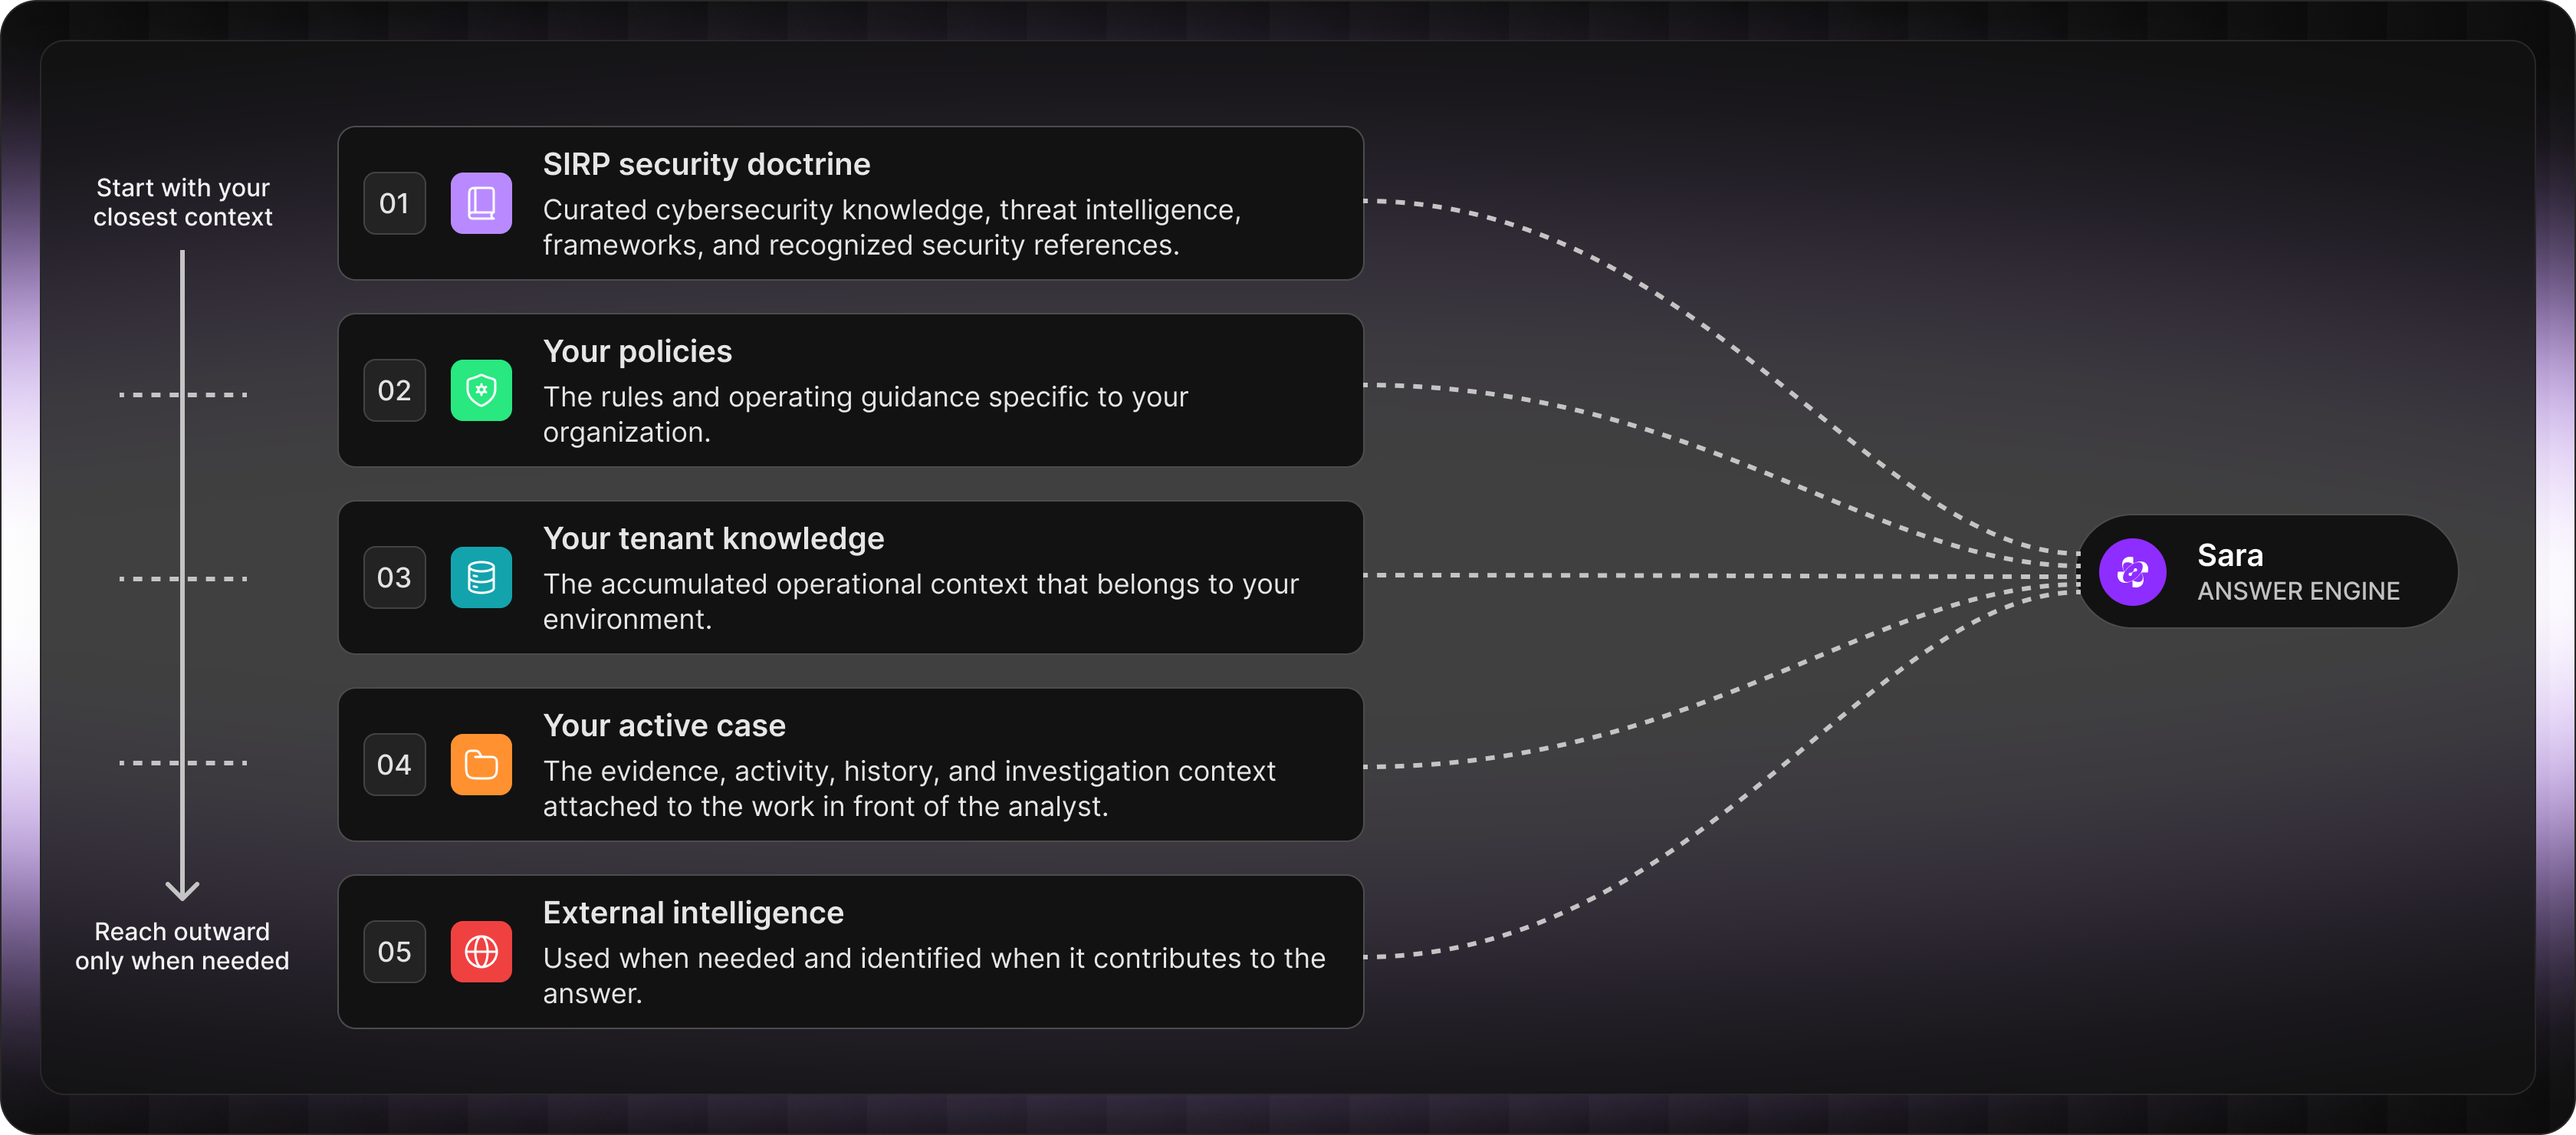
Swipe to explore the diagram
When the evidence is not strong enough, Sara says so instead of filling the gap.
A general security question and a live investigation are different problems. Sara changes the context it uses to match what your analyst is trying to understand, investigate, or hunt.
Security knowledge from SIRP curated doctrine and recognized security references.
Ask: What does APT38 typically target?
Questions about your own environment in plain language, using approved and auditable data paths.
Ask: Show me my P1 incidents.
Investigation help with the active case, evidence, analyst activity, and relevant history already in context.
Ask: Why is isolation recommended here?
Threat intelligence turned into a structured HuntPlan with hypotheses, data sources, time windows, and MITRE ATT&CK techniques.
Ask: Can we hunt for Lazarus Group in our environment?
Why an alert was closed. What an analyst tried. Which evidence changed the verdict.
Sara keeps that context where analysts work, so it survives the shift change.
When L1 escalates, L2 gets the evidence, previous work, open questions, and artifacts with the case. No cold restart.
The same incident type is evaluated against the same published knowledge and operating guidance, whoever is on shift.
Analysts propose updates to tenant knowledge. Senior analysts review them before they become shared operational context.
New analysts ask about policies, previous incidents, and recommendation logic while they work, instead of waiting for a senior.
Why a similar alert was closed, what an analyst tried, and which evidence changed the verdict are there on the next case.
AI inside a SOC should not create a new blind spot. You can see what Sara
accessed, what it answered, and what the analyst decided.
Sara checks the analyst role on every message. Cross-tenant information is outside its retrieval scope.
Messages, retrieved context, recommendations, and analyst decisions are logged for review and audit.
Incidents, alerts, conversations, and tenant knowledge are not used to update the model weights.
Sara runs through the OmniSense region serving the customer jurisdiction, with customer data kept inside that regional boundary during reasoning.
Paste in an alert, IOC, CVE, or suspicious email and Sara triages it. Free, with no account and no signup. Inside OmniSense, Sara works on your cases with your context.
Autonomous, governed security operations powered by OmniSense™.